Disclaimer: Information found on CryptoreNews is those of writers quoted. It does not represent the opinions of CryptoreNews on whether to sell, buy or hold any investments. You are advised to conduct your own research before making any investment decisions. Use provided information at your own risk.
CryptoreNews covers fintech, blockchain and Bitcoin bringing you the latest crypto news and analyses on the future of money.

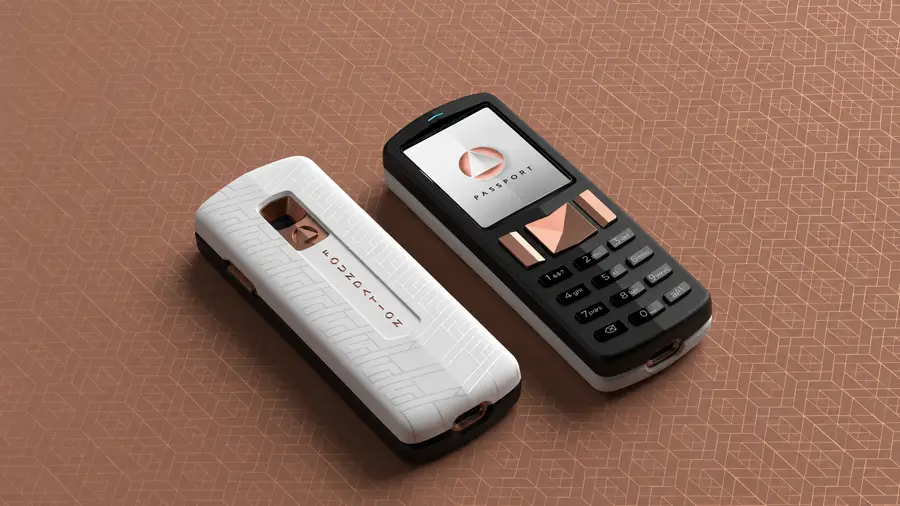
Foundation, the developer of Passport hardware wallets, alerted customers that attackers sent emails appearing to come from the company’s official domains. The breach was caused by compromised API keys from the hosting provider Cloudflare.
Unlike typical phishing, where attackers send emails from addresses mimicking official ones, the unknown actors gained access to systems linked to Foundation’s actual domains. Foundation co-founder and CEO Zach Herbert stated that the server infrastructure was compromised due to a vulnerability in one of the company’s applications. Foundation believes the attackers may have obtained customer email addresses from previously leaked user databases or from information related to recent orders placed through the company’s Shopify store.
Foundation announced that the malicious domain mentioned in the phishing emails has been blocked and the Cloudflare API keys have been revoked. The company stopped the unauthorized email blast within 10 minutes of receiving reports from users, cutting off the attackers’ access to its systems.
Related Posts
The Foundation team is currently investigating whether access was gained to customer support correspondence and personal customer data. Passport manufacturer Foundation assured users that its hardware wallets and the funds stored on them remain secure. Since private keys remain isolated from internet-connected devices, the compromise of the email infrastructure does not mean the wallets or keys have been hacked. However, wallet owners could lose their crypto assets if they disclose their seed phrase via fake websites or applications.
Foundation did not specify exactly how many phishing emails were sent. The company did not disclose the content of the phishing emails nor did it report whether wallet owners entered their seed phrases or other confidential information after receiving the messages. Foundation promised to publish a detailed incident report.
In September, hardware wallet manufacturer Trezor also reported that hackers had breached an email service provider’s system to send phishing emails from an official email address. The hackers attempted to scare users by claiming a serious vulnerability had been found in Trezor wallets and to trick them into clicking a suspicious link.
